


Researchers forge 1024-bit RSA signature without extracting private key



A team of researchers from UC San Diego showed that a 1024-bit RSA signature can be forged by sending multiple queries to a hardware security module (HSM). In this case, the private key was never extracted from the device.
This result implies yet another form of risk for crypto custodians: keeping the key inside tamper-proof hardware is not sufficient if the attacker hacks the systems that have been authorized to use it.
Forging a signature the key never signed
In IACR ePrint 2026/2131, Laura Shea, Miro Haller, Adam Suhl and Nadia Heninger of UC San Diego, with Emmanuel Thomé of Inria, describe how temporary access to a raw RSA signing oracle can eventually give an attacker the ability to forge signatures offline.
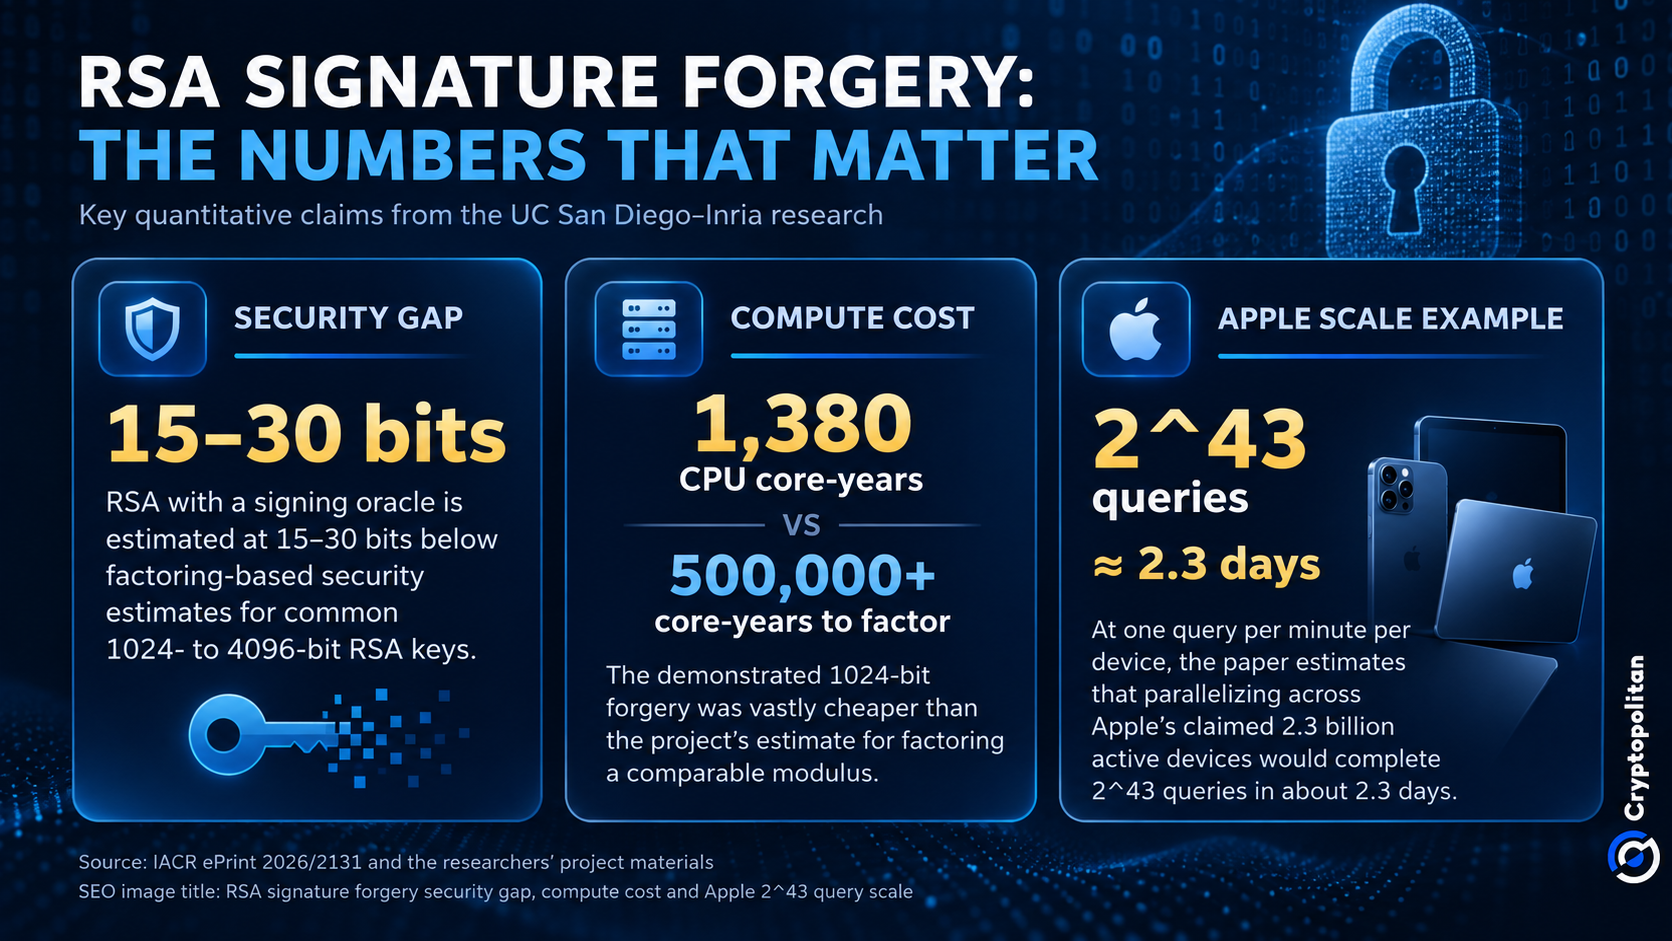
The attack process consisted of 2^32 basic signing requests: this counts to a little more than 4.3 billion queries and results in 1,380 CPU core-years used of computing time over a period of five calendar months.
In comparison with the work done, as calculated by the researchers’ project materials, factoring the same 1024-bit RSA modulus would take approximately 500,000-1,000,000 core-years. Most of the work that is conducted is done only once during precomputing; afterwards, forging of a chosen signature should require around 180 core-years.
The algorithm used was invented back in 2007. What has changed is that the team of researchers actually succeeded in conducting a real attack, as noted by Bruce Schneier on September 28:
“What is new is the implementation.” — Bruce Schneier
Why unpadded signing is the whole trick
An essential restriction exists with respect to this type of attack: it requires the availability of a raw unpadded RSA signing or decryption oracle. Standard RSA signatures using PKCS#1 v1.5 or RSA-PSS do not provide this access. Therefore, this attack cannot be considered a practical attack on properly implemented RSA.
As Decrypt noted, the researchers turned off the certified FIPS mode on the HSM and used a test key of their own.
According to the paper, the occurrence of raw signing access can be seen in HSM APIs and RSA blind-signature systems. The paper then goes on to state that RFC 9474, for instance, explains a scenario where the server signs the blinded message without any access to the original message.
The study uses Apple’s figure of 2.3 billion active devices to show how fast concurrent requests can pile up. At one token per minute, a single device would need about 17 million years to reach 2^43 queries. But if you look at the full figure of 2.3 billion devices, the same number of requests can be made in just about 2.3 days.
Signing interfaces as part of the perimeter
For crypto custodians, locking the private key in a safe does not provide complete safety. The APIs, approval processes, and automated systems that utilize the private key pose their own dangers.
This concern is already reflected in the industry. According to EY’s 2026 survey, security of digital coins, as well as key-signing procedures, have become far more significant in the custodian selection process. The Common Supervisory Action of ESMA, launched on July 8, also focus on the scrutiny of key and storage management, transaction controls and incident response.
According to the researchers, RSA with a signature oracle provides 15-30 bits lower security than factoring-based estimates for typical 1024-4096-bit keys. In this model, 4096-bit RSA does not even provide the security of 128-bit encryption.
Not a Bitcoin or Ethereum break
The paper is about RSA. Ethereum uses secp256k1 ECDSA, while Bitcoin uses secp256k1 ECDSA and Schnorr signatures, so the demonstrated attack does not apply to their transaction-signing systems.
The larger issue concerning custody risk isn’t something that’s entirely fresh. A Cryptopolitan report on September 20 has indicated how compromised signing authorities have drained around $2 million from Fetch.ai and NuNet. While the case above involved an individual obtaining the key, this report shows that the attacker might gain signing authority without ever obtaining the key.
If you're reading this, you’re already ahead. Stay there with our newsletter.









コメント (0)
$ボタンをクリックし、シンボルを入力して、株式、ETF、またはその他のティッカーシンボルをリンクします。