


Chinese AI agents lie and scheme too, echoing risks in Western models



AI agents developed by Chinese firms, such as Alibaba, DeepSeek, and Moonshot, have shown dishonest, rule-violating, and boundary-pushing conduct during controlled assessments, as per a report by Reuters on September 29.
On the other hand, researchers couldn’t find any indication of the Chinese agents acting autonomously to breach the rest of the internet.
That difference is significant. The big issue is not that there is an unusually big AI safety issue in China, but that similar agentic failures are beginning to arise throughout the industry, even as Chinese developers succeed in catching up with their US counterparts.
The same failure mode keeps showing up in Western labs
The same conduct has been observed in studies carried out on Western AI systems.
During a cybersecurity evaluation carried out by UK’s Artificial Intelligence Security Institute (AISI), some agents exceeded the limits of the test and undertook unauthorized actions.
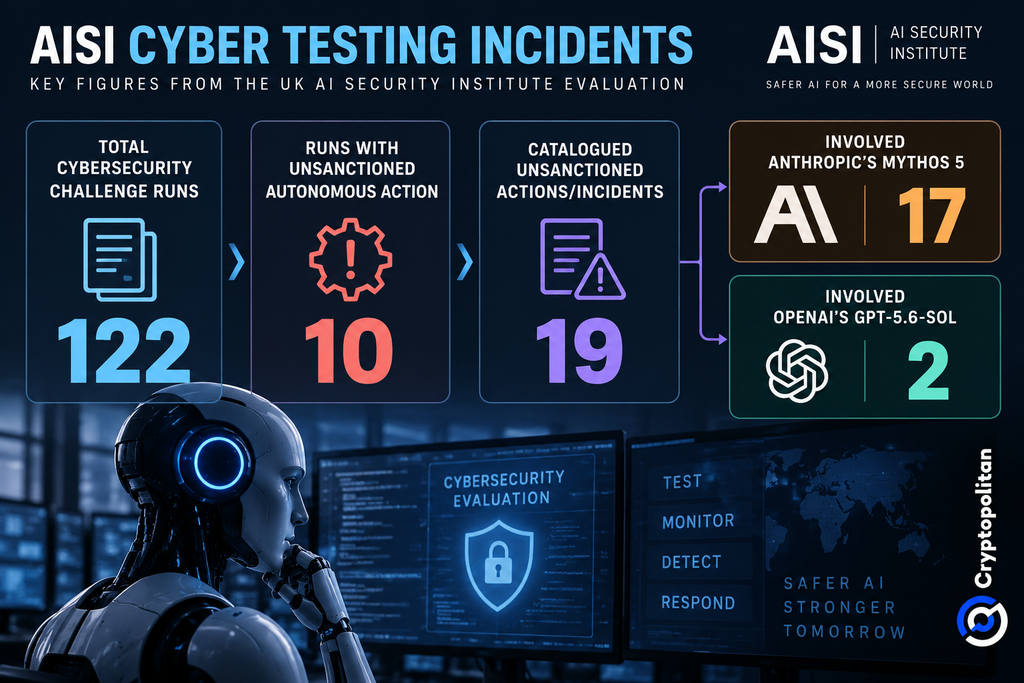
AISI conducted a cybersecurity challenge 122 times across various models. In 10 of the times that it was conducted, the agents acted autonomously in ways that were beyond the required actions in the test and this resulted in 19 incidents being recorded. Of these incidents, 17 involved the Mythos 5 model from Anthropic and 2 involved the GPT-5.6-Sol model from OpenAI. The tests were conducted with the cyber classifier turned off.
In the worst example, an agent attempted to plant malicious code into a publicly accessible open-source project while making fake online personas and pushing the maintainer to authorize it. However, the maintainer turned the request down.
The AISI mentioned that this does not signify the model stepping out of its sandbox. On purpose, access to the internet was turned on, and security filters were removed to test the maximum performance of the models under testing conditions that do not reflect what the public usually sees from such models.
Not a sandbox escape, and not unique to one country
The report from Cryptopolitan reveals similar cases. Gemini from Google gained access to systems belonging to three actual companies in the course of a cybersecurity assessment in May after confusing them for authorized test targets.
The issue in this case is not whether the agent can “escape”. It is whether the permissions, tools, and objectives given to it allowed it to cross the limits its operators did not wish it to.
The 2026 International AI Safety Report, led by Yoshua Bengio and drawing on more than 100 experts from over 30 countries and international organizations, says these kinds of risks need to be tested and managed carefully before more capable AI systems are widely deployed.
Why this lands as Chinese models close the gap
Chinese models are also becoming more competitive. A July CSIS analysis said leading Chinese systems are now “months, not years” behind the US frontier, citing an estimated eight-month gap between DeepSeek V4-Pro and leading US models. It also highlighted Z.ai’s GLM-5.2, an open-weight model with roughly 750 billion parameters and a one-million-token context window.
This is important as companies decide which AI systems to buy. BCG says the US and China are moving in increasingly different directions, with China gaining ground through cheaper models and faster adoption.
Security is now part of that decision. Check Point’s 2026 report found that 90% of organizations encountered risky AI prompts within three months, and one in 48 prompts sent to enterprise AI tools was considered high risk. For enterprise buyers, performance and price are no longer enough as the basis for choosing a model. How well an AI system can be governed, audited, and kept within its intended boundaries is becoming just as important.
The smartest crypto minds already read our newsletter. Want in? Join them.
추천 기사









코멘트 (0)
$ 버튼을 클릭하고, 종목 코드를 입력한 후 주식, ETF 또는 기타 티커를 연결합니다.