


Researcher cracks an unpatched PHP server and takes its $2,000 Bitcoin prize in 19 hours


A security researcher was able to exploit an intentionally unpatched PHP server and claim its Bitcoin bounty in just over 19 hours.
The public stunt was a test to see if the recent PHP2Shell flaws are as dangerous as they are said to be.
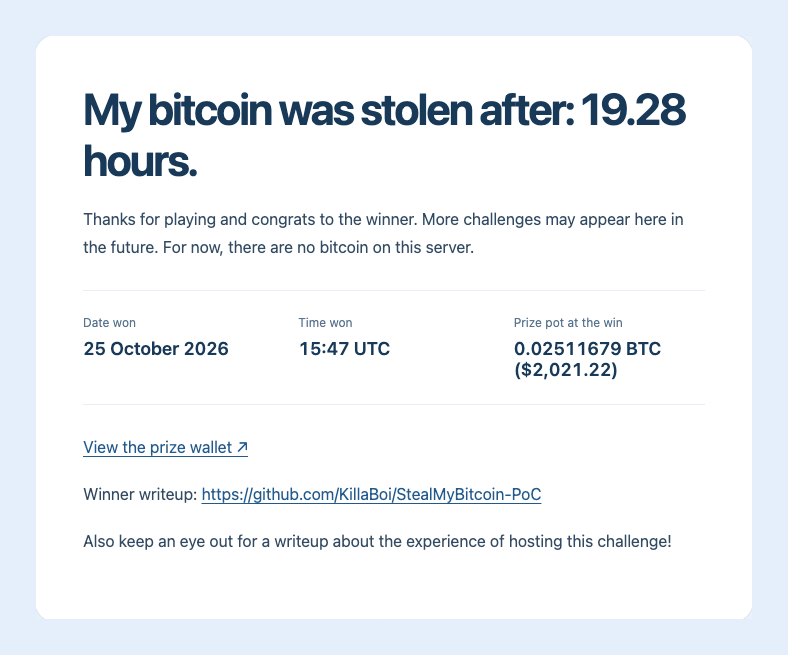
Stealmybitcoin.com logged the win at 15:47 UTC on October 25
Stealmybitcoin.com, the site where the game was hosted, verified the bounty had been claimed. Its results page shows the Bitcoin was taken after 19.28 hours, with the win being logged at 15:47 UTC on Sunday, October 25.
The prize pot was 0.02511679 BTC, worth $2,021.22 at that time. The page reads: “For now, there are no bitcoin on this server,” adding that more challenges may follow.
The winner, who goes by the handle KillaBoi, posted a proof-of-concept write-up to GitHub. The target was running PHP 8.4.26.
The write-up says that the one private key it recovered did not derive the prize address shown on the homepage. It calls this a mistake by the creator, acknowledged via email, and the site still lists the challenge as won.
The contest was also seen by more people through the @hackerfantastic account, which is connected to the company hacker.house. In a post on October 25, the account explained how the challenge worked.
The win follows emergency PHP2Shell fixes on October 21
The experiment came days after a scramble over two critical bugs in PHP. Details of the vulnerabilities leaked online, prompting PHP’s maintainers to ship emergency fixes on October 21, a day ahead of schedule, as Cryptopolitan reported.
The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619 and dubbed PHP2Shell, both received a severity score of 9.2 out of 10 and enable remote code execution on unpatched servers.
PHP is used by about 70% of sites that have a known server-side language, and many sites shut down as a precaution. Finland, the Netherlands and France all temporarily pulled government websites offline.
Cloudflare said it saw millions of what it called exploitation attempts in the hours after the bugs were made public.
Two months were given to a coalition that included OpenAI to make fixes. OpenAI said that the same AI tools that found the flaws could also help attackers quickly make exploits.
The operator of the site has promised a separate write-up of the experience of hosting it.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
Recommended Articles




Comments (0)
Click the $ button, enter the symbol, and select to link a stock, ETF, or other ticker.