


Sakura Internet moved on PHP flaws hours before Japan's PM


Sakura Internet froze part of its cloud service Wednesday because of two critical PHP flaws.
Later that day, Prime Minister Sanae Takaichi called on website operators to patch that night or shut down their sites temporarily.
Database Appliance loses phpMyAdmin with no restart date
Sakura’s notice, published at 1:22 p.m. Japan time on October 21, is withdrawing the web UI tools from its Database Appliance service. Those tools are phpMyAdmin, phpPgAdmin and pgAdmin.
The Database Cluster service is still up. Sakura did not give a date for the restart and, in the interim, pointed customers to SQL clients compatible with MariaDB and PostgreSQL.
The company apologized to customers for the interruption.
Cygames and pixiv also declared emergency maintenance about the PHP flaws. PHP is widely used in e-commerce and other web applications.
Japan’s prime minister pointed operators to the 11 p.m. fix
Takaichi’s appeal was posted on X at 9:55 p.m. Japan time. She said it was a very pressing request for action that night and asked operators to verify whether their public websites were using PHP.
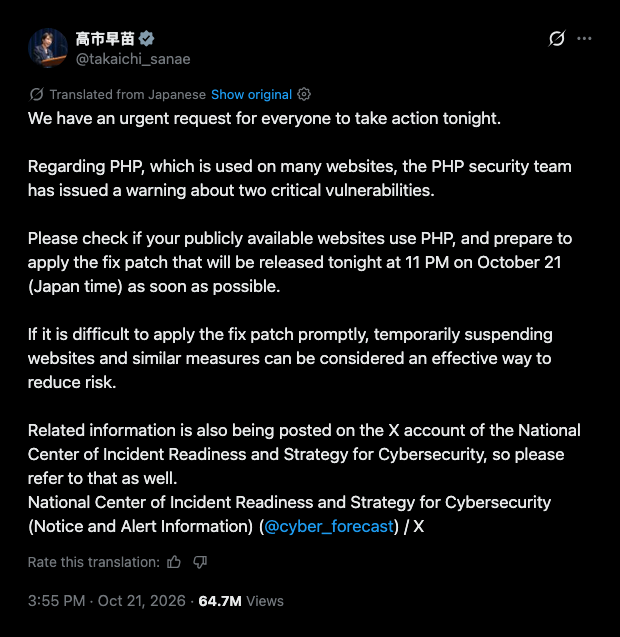
She told them to prepare to roll out the patch due at 11 p.m. Japan time. Taking a website offline temporarily was one way to reduce risk if quick patching was tricky, she wrote.
She also directed followers to the National Cybersecurity Office’s account on X.
The office said at 10:57 p.m. that the updates were out and urged users to install them as soon as possible. The office warned that unpatched sites could be breached.
By Thursday, Takaichi’s post had picked up more than 308,000 likes and about 78,000 reposts.
Fixed versions: PHP 8.2.35, PHP 8.3.36, PHP 8.4.27, PHP 8.5.12.
According to Cryptopolitan, details leaked, so PHP’s maintainers shipped the fixes a day early. The two flaws, dubbed “PHP2Shell” and identified as CVE-2026-109618 and CVE-2026-109619, each earned a 9.2 out of 10 score and could allow hackers to execute code on unpatched servers.
The first bug exploits how PHP deals with out-of-memory conditions. The second exploits request state that survives after its memory is freed.
The advisory from PHP puts all installations that serve web requests at risk. That covers PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed.
The project ranks mod_php as the riskiest setup, and there is a demonstrated exploit that fires before any application code runs. Linux distributors and long-term-support vendors were shipped the patches in advance.
No further updates for PHP 8.1 and below come from the project. The security team still put out minimal source backports for PHP 7.4, 8.0 and 8.1.
About 70% of all websites whose server-side language is known use PHP. Japan, the EU, the US, Germany, Australia and the UK also issued warnings.
Finland, the Netherlands and France took government websites offline as a precaution. Nintendo pulled services to patch.
If you're reading this, you’re already ahead. Stay there with our newsletter.
Recommended Articles




Comments (0)
Click the $ button, enter the symbol, and select to link a stock, ETF, or other ticker.